APT·위협행위자 관련 소식
국내 보안기업 분석을 앞에 둡니다 — 글로벌 매체는 하루 수십 건씩 쏟아지지만 국내 분석은 주 단위라, 최신순으로만 뽑으면 국내 글이 영영 화면에 안 나옵니다. 본문은 복제하지 않고 링크와 발췌만 드립니다.
APT·위협행위자
발행일 최신순
 2026년 8월 APT 공격 동향 보고서(국내)개요 안랩은 자사 인프라를 활용해 국내 타겟의 APT(Advanced Persistent Threat) 공격을 모니터링했다. 본 보고서는 2026년 8월 한 달 동안 확인된 국내 APT 공격의 유형과 통계를 정리한 내용이다. APT 국내 공격 동향 국내에서 확인된 APT 공격의 대부분은 Spear Phishing(특정 개인이나 집단을 노린…ASEC 분석 리포트국내6일 전피싱·사기APT·위협행위자
 팔로알토 네트웍스, 유닛42 지속형 프런티어 AI 디펜스 발표팔로알토 네트웍스가 AI를 활용해 기업의 보안 취약점을 상시 탐지하고 해결하는 유닛42 지속형 프런티어 AI 디펜스를 발표했다.이번 서비스는 앤트로픽의 클로드 미토스와 오픈AI의 GPT를 비롯한 고성능 모델을 기반으로 작동하며, 공격자가 취약점을 실제 공격에 악용하기 전에 기업이 선제적으로 대응할 수 있도록 돕는다.오늘날 위협 행위자는 A…데일리시큐국내6일 전취약점·패치APT·위협행위자
 2026년 8월 다크웹 위협 행위자 동향 보고서알림 2026년 8월 다크웹 위협 행위자 동향 보고서는 핵티비스트를 포함해 딥웹과 다크웹에서 활동하는 위협 행위자의 동향을 중심으로 작성되었다. 일부 내용은 사실 관계를 확인할 수 없다고 명시되었다. 주요 이슈 NoName057(16), BD Anonymous, Dark Storm Team은 일본의 정부기관, 지방자치단체, 운송, 금융, …ASEC 분석 리포트국내22일 전APT·위협행위자
 구글, 2026년 2분기 AI 위협 추적 보고서 발표...에이전틱 AI 악용 증가구글위협인텔리전스그룹(GTIG)이 2026년 2분기 최신 AI 위협 동향을 분석한 'AI 위협 추적 보고서(AI Threat Tracker)'를 공개했다.이번 보고서는 위협 행위자들이 공격 라이프사이클 전반에서 작전을 고도화하기 위해 AI를 활용하는 양상을 조명했다. 공격자들의 에이전틱 AI 활용은 실험실 단계를 넘어 취약점 발견 영역을 …데일리시큐국내26일 전취약점·패치유출·침해
 기능별 C2 서버를 운용하는 Kimsuky 그룹의 새로운 LNK 악성코드 등장[이미지] 생성형 AI 제작 명령 전달과 감염 알림, 정보 유출을 서로 다른 정상 서비스에 분산시킨 악성 LNK(바로가기) 파일이 국내 금융 문서로 위장해 유포된 정황이 확인되었습니다. 해당 파일은 PDF 아이콘과 문서 속성 정보를 사용해 정상 문서로 위장하고 있으며, 실행 시 배치 스크립트를 단계적으…이스트시큐리티 알약 블로그국내26일 전유출·침해APT·위협행위자
 또 김수키? 이번엔 수산 식자재 구매 요청서로 위장수산 식자재 구매를 검토해 달라는 요청서가 도착했다. 파일을 열면 정상 HWP 문서가 나타나지만, 사용자가 내용을 확인하는 사이 뒤에서는 악성 스크립트가 실행되고 예약 작업까지 등록된다. 이후 시스템 정보를 외부로 빼내고 추가 명령을 내려받아 실행하며 흔적까지 지운다. 정상 업무 문서를 앞세워 공격을 감춘 김수키(Kimsuky) 연관 악성…ASEC 분석 리포트국내1개월 전APT·위협행위자악성코드2026년 7월 APT 공격 동향 보고서(국내)개요 안랩은 자사 인프라를 활용해 국내 타겟의 APT(Advanced Persistent Threat, 지능형 지속 공격) 공격을 모니터링했다. 이 보고서는 2026년 7월 한 달 동안 확인된 국내 APT 공격의 분류, 통계, 유형별 기능을 정리한 내용이다. APT 국내 공격 동향 국내에서 확인된 APT 공격의 대부분은 Spear Phis…ASEC 분석 리포트국내1개월 전피싱·사기APT·위협행위자2026년 7월 APT 그룹 동향 보고서목적 및 범위 2026년 7월 APT 그룹 동향 보고서는 국가 지원 위협 조직과 금전적 이익형 공격자가 공급망 공격, 계정 탈취, 클라우드 침해, 사회공학 기법을 복합적으로 활용하는 흐름을 정리한 자료다. 주요 표적은 Microsoft 365, 웹 메일 계정, 클라우드 인프라, GitHub 및 개발 환경, VPN·원격접속 시스템, 모바일 …ASEC 분석 리포트국내1개월 전유출·침해APT·위협행위자
 2026년 7월 다크웹 위협 행위자 동향 보고서알림 2026년 7월 다크웹 위협 행위자 동향 보고서는 핵티비스트를 포함해 딥웹 및 다크웹에서 활동하는 위협 행위자의 동향을 중심으로 작성되었다. 일부 내용은 사실 관계를 확인할 수 없다고 명시되었다. 주요 이슈 Handala는 북미 지역 인터넷 서비스 제공업체의 핵심 인프라를 침해해 대규모 인터넷 장애가 발생했다고 주장했다. BD Ano…ASEC 분석 리포트국내1개월 전유출·침해APT·위협행위자2026년 6월 APT 공격 동향 보고서(국내)내용 안랩은 자사 인프라를 활용해 국내 타겟 APT(Advanced Persistent Threat, 지속적으로 은밀하게 진행되는 공격) 공격을 모니터링했다. 본 보고서는 2026년 6월에 확인된 국내 APT 공격의 분류와 통계를 정리하고, 유형별 기능을 설명한다. 목적 및 범위 국내에서 확인된 APT 공격의 대부분은 Spear Phish…ASEC 분석 리포트국내2개월 전피싱·사기APT·위협행위자
 Kimsuky 그룹의 외교 관련 종사자 사칭 공격 사례 (PebbleDash, PrxClient)AhnLab SEcurity intelligence Center(ASEC)은 과거 “PebbleDash와 RDP Wrapper를 악용한 Kimsuky 그룹의 최신 공격 사례 분석”[1] 포스팅을 통해 스피어 피싱 공격을 사용해 PebbleDash 악성코드를 설치하는 공격 사례를 공개하였다. 동일한 공격자는 2026년에…ASEC 분석 리포트국내2개월 전피싱·사기APT·위협행위자
 "개인정보가 유출된 것 같아요"… 보안 담당자를 노린 김수키(Kimsuky) 스피어 피싱 공격 안녕하세요, 이스트시큐리티 입니다. "제 개인정보가 유출된 것 같아요." 업무 중 고객으로부터 위와 같은 문의 메일을 받게 된다면 어떻게 행동해야 할까요? 아마 대부분은 사실 여부를 확인하기 위해 다급히 첨부파일이나 링크를 확인해 볼 것입니다. 최근 발견…이스트시큐리티 알약 블로그국내3개월 전피싱·사기유출·침해
 개인정보 유출 의심 문의로 위장한 Kimsuky 스피어피싱 사례 분석[이미지] 생성형 AI 제작 이스트시큐리티 대응센터(ESRC)에서 운영 중인 APT TDS(Threat Detection System)를 통해, "개인정보 유출 의심 확인 요청"이라는 민감한 소재로 위장한 스피어 피싱 공격이 포착되었습니다. [그림 1] TDS 이메일 모니터링 시스템에서 탐지된 피싱 메…이스트시큐리티 알약 블로그국내3개월 전피싱·사기유출·침해
 배상민 ESRC 실장 인터뷰 "해커들, 이제는 회사와 비슷한 형태 갖춰"안녕하세요. 이스트시큐리티입니다. AI 기술의 발전과 함께 사이버 위협 환경도 빠르게 변화하고 있습니다. 랜섬웨어 조직을 비롯한 공격 그룹들은 점차 조직화·전문화되고 있으며, AI를 활용해 공격의 속도와 정교함을 높이고 있는데요. 이와 관련해 이스트시큐리티 시큐리티대응센터(ESRC) 배상민 실장이 최근…이스트시큐리티 알약 블로그국내4개월 전랜섬웨어피싱·사기
 Adobe Reader 제로데이 취약점을 이용한 악성 PDF 공격 주의![이미지] 생성형 AI 제작 최신 버전의 Adobe Reader 제로데이 취약점을 악용한 정교한 PDF 공격이 확인되었습니다. 이번 공격은 단순한 악성코드 실행을 넘어, 피해…이스트시큐리티 알약 블로그국내5개월 전취약점·패치유출·침해
 GitLab 플랫폼을 이용한 Kimsuky 공격 사례[이미지] 생성형 AI 제작 이스트시큐리티 대응센터 (ESRC) 에서 운영 중인 APT TDS(Threat Detection System) 에서는 최근 이력서 및 대북 정책 문서로 위장한 악성 LNK( 바로가기 ) 파일의 유포 정황을 포착했습니다 . TDS 에서 탐지된 악성 LNK 파일은 …이스트시큐리티 알약 블로그국내6개월 전APT·위협행위자악성코드
 베트남 위협행위자의 PyChain 캠페인 : 저작권 경고 이메일로 시작한 글로벌 피싱의 기술적 진화 “귀하의 저작권 침해가 확인되었습니다 .” 한 줄로 시작되는 이메일이 최근 기업 담당자들의 수신함에 자주 들어오고 있습니다 . 겉으로는 법적 경고처럼 보이지만 , 실제로는 피싱 공격의 출발점입니다 . 이스트시큐리티 대응센터 (ESRC) 는 이 캠페인을 1 년 넘게 추적해 왔으며 , 그 과정에서…이스트시큐리티 알약 블로그국내6개월 전피싱·사기유출·침해
 고용노동부 사칭 피싱 유포 사례 분석 - 이메일 도메인 분석까지 수행하는 ‘정밀 타겟형’ 공격 최근 이스트시큐리티 대응센터 (ESRC) 에서 운영 중인 APT TDS(Threat Detection System) 를 통해 , 네이버웍스 사용자를 겨냥한 고도화된 피싱 공격이 포착되었습니다 . 이번 공격은 단순 유포형 피싱을 넘어 기업의 메일 환경을 식별하는 정밀…이스트시큐리티 알약 블로그국내8개월 전피싱·사기APT·위협행위자ScarCruft’s New Language: Whispering in PubNub, Crafting Backdoor in Rust, Striking with RansomwareAuthor : Jiho Kim, Jaeki Kim | S2W TALON Last Modified : Aug 07, 2025 Photo by Simon Infanger on Unsplash The full report is available at the following link. PDF> ScarCruft’s New Language…S2W Blog국내1년 전랜섬웨어APT·위협행위자Warlock Exploits SharePoint Flaws to Disable Security Tools and Deploy RansomwareThe suspected China-linked threat actor known as Warlock is still continuing to weaponize Microsoft SharePoint vulnerabilities, likely both old and new, in attacks targeting organizations in…The Hacker News2일 전랜섬웨어취약점·패치
 Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage CampaignGovernment and policy organizations across Asia have become the target of a new campaign orchestrated by a China-nexus threat actor. The activity, which has targeted government and policy or…The Hacker News3일 전피싱·사기APT·위협행위자
 Microsoft says threat actors are ahead in the early AI raceMicrosoft says cyberattackers are currently benefiting from artificial intelligence faster than defenders, allowing threat actors to speed up vulnerability discovery, malware development, an…BleepingComputer4일 전취약점·패치APT·위협행위자
 WordPress Backdoor Rebuilds Itself After Cleanup Using Files, Database, and Shared MemoryCybersecurity researchers have shed light on a WordPress compromise in which threat actors deployed multiple persistence mechanisms to ensure that the final payload kept returning without ha…The Hacker News4일 전APT·위협행위자악성코드
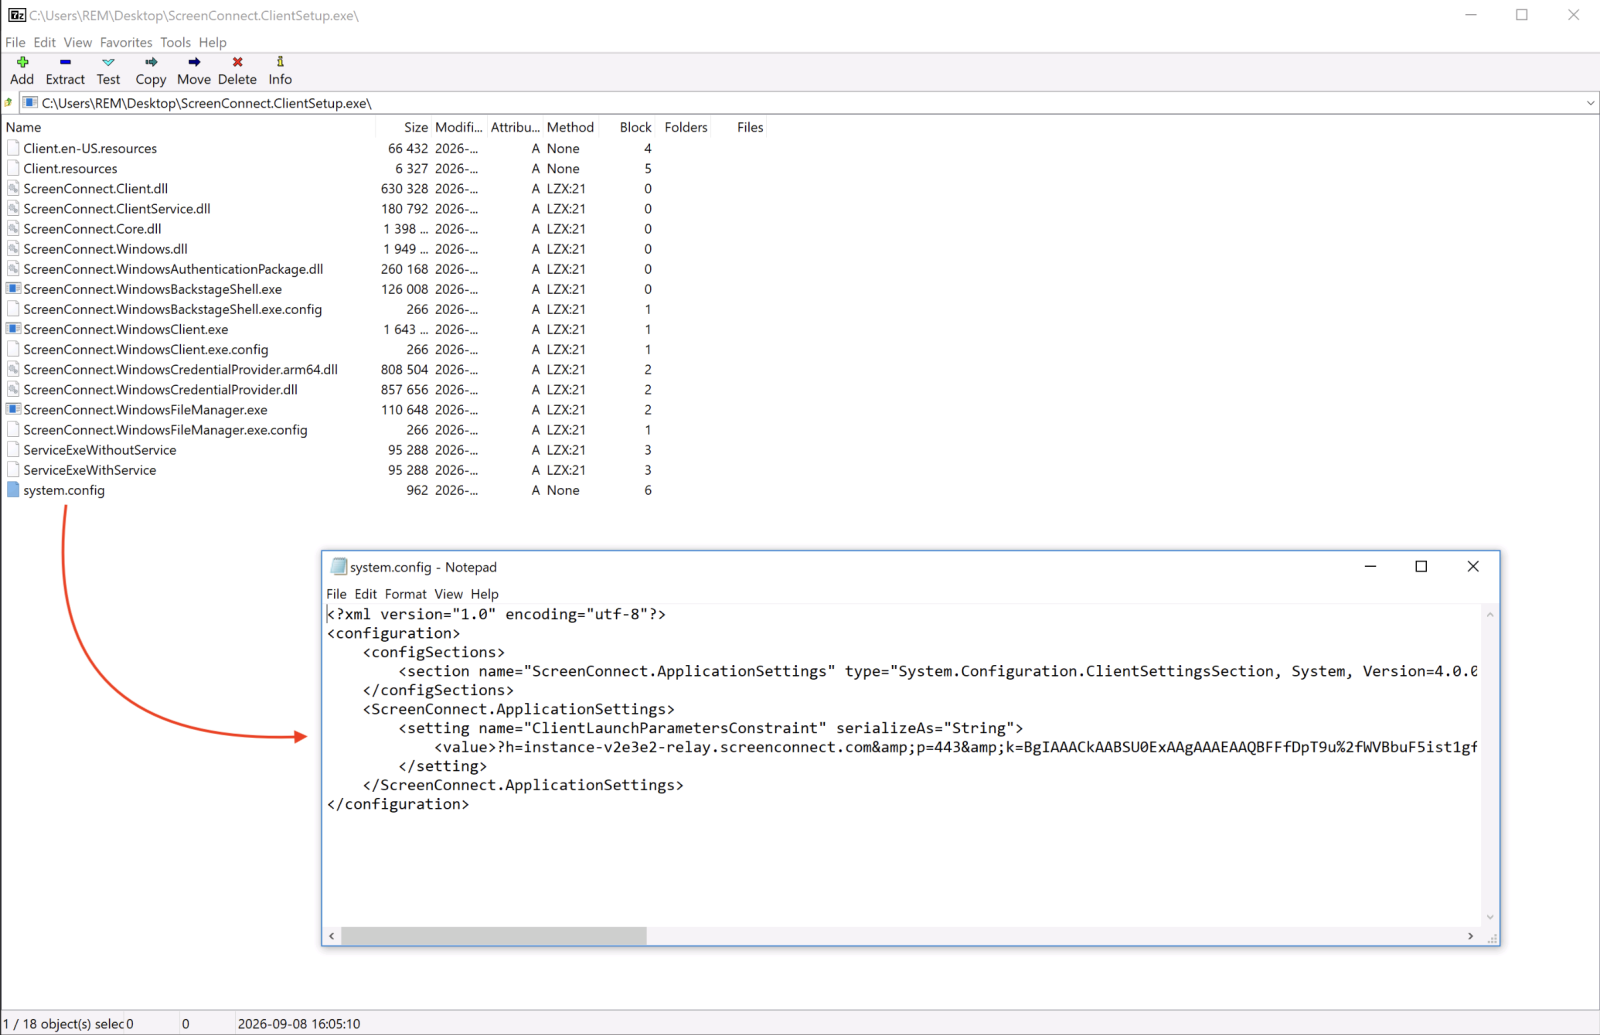 ScreenConnect Client (Ab)used by Attackers, (Thu, Oct 1st)Threat Actors do not always use top-notch techniques or very complex malware to perform their attacks. Sometimes, they just abuse of existing applications... I received a very simple phishin…SANS Internet Storm Center4일 전피싱·사기APT·위협행위자
 Citrix NetScaler Post-Exploitation Payload Creates Superuser, Maps Web Shell to CSS-Like URLsThreat actors have been observed exploiting a critical pre-authentication command injection vulnerability in Citrix NetScaler ADC and NetScaler Gateway to drop web shells and attempt theft o…The Hacker News4일 전취약점·패치APT·위협행위자
 WatchGuard fixes critical Fireware OS flaw allowing remote code executionWatchGuard fixes 15 Fireware OS flaws, including a critical RCE bug that could give attackers root access to vulnerable Firebox appliances. WatchGuard has released security updates for Firew…Security Affairs5일 전취약점·패치APT·위협행위자CVE-2026-86131
 Attackers Exploit Zimbra Flaw to Deploy Web Shells and Harvest Authentication SecretsThreat actors have weaponized a now-patched security flaw in Zimbra Collaboration Suite (ZCS) to deploy web shells and access mailbox data, according to findings from the Microsoft Security …The Hacker News5일 전취약점·패치APT·위협행위자CVE-2026-73570
 Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix LuresThreat actors are abusing ChatGPT Custom GPTs to disguise them as legitimate product offerings and direct unsuspecting victims to malicious sites that employ ClickFix lures to deliver malwar…The Hacker News5일 전APT·위협행위자악성코드
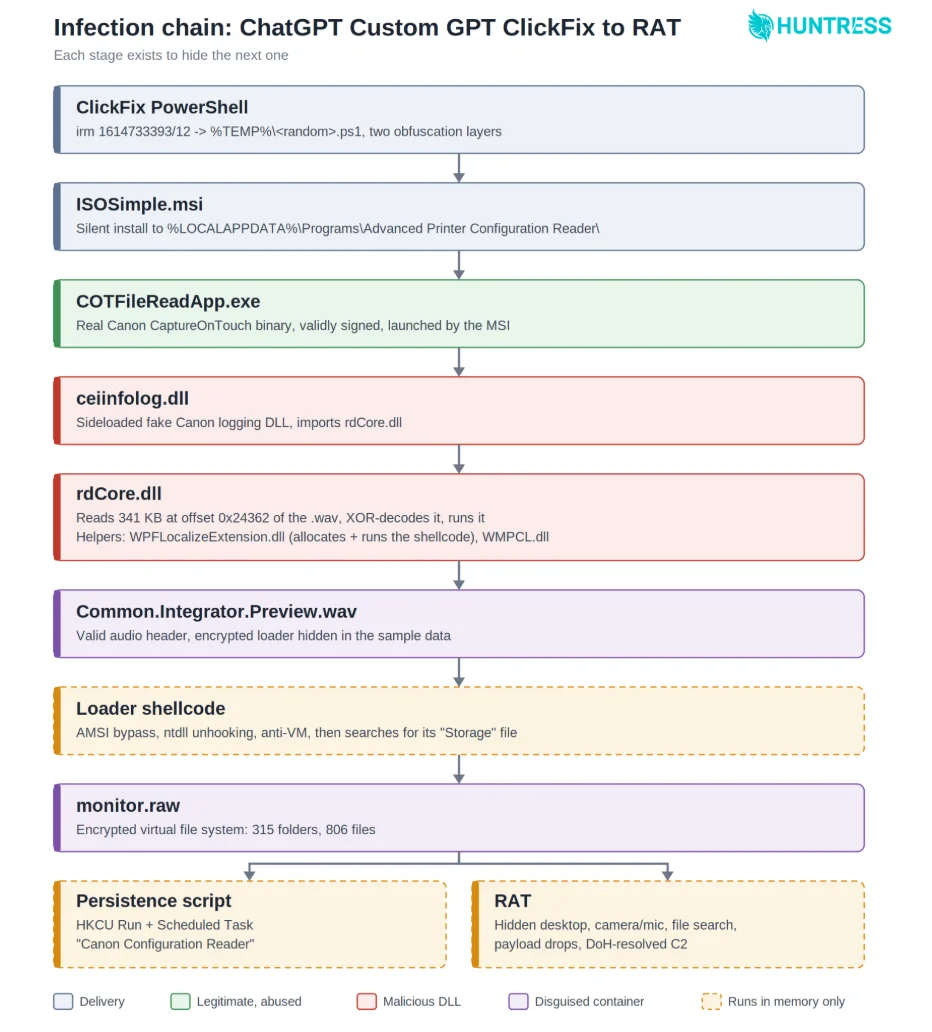 Attackers Abuse ChatGPT Custom GPTs to Deploy a Full-Featured RATThreat actors abused fake ChatGPT Custom GPTs and ClickFix to deliver a multi-stage RAT . ChatGPT’s Custom GPT feature is the latest legitimate surface being turned into a delivery mec…Security Affairs5일 전APT·위협행위자
 Attackers Exploit NetScaler Flaw for Root Access, Deploy WHIPSHOT and SLAPSHOTUnknown threat actors have been observed exploiting a newly patched security flaw in Citrix NetScaler ADC and NetScaler Gateway appliances to target organizations in North America and Europe…The Hacker News5일 전APT·위협행위자
 JADEPUFFER-Linked Attackers Used Compromised Service Principals to Delete Azure ResourcesThe threat actor known as JADEPUFFER has been observed orchestrating destructive actions within a Microsoft Azure environment using compromised service principals. Microsoft, which is tracki…The Hacker News7일 전APT·위협행위자클라우드·인프라
 ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacksThe ShinyHunters extortion gang is using a URL-encoding trick to bypass web application firewall rules that mitigate the Oracle PeopleSoft CVE-2026-35273 flaw, allowing the threat actors to …BleepingComputer9일 전취약점·패치APT·위협행위자CVE-2026-35273
 Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber AttackKiteworks (formerly Accellion) is urging customers to shut down their systems as a precautionary measure for nine hours over the weekend after it received threat intelligence about an immine…The Hacker News9일 전APT·위협행위자
 Cryptocurrency exchange Bitget Says North Korea-Linked Hackers Stole $351.6 MillionBitget says suspected North Korea-linked actors stole $351.6M from hot and warm wallets. Withdrawals were suspended while Mandiant investigates. Cryptocurrency exchange Bitget says suspected…Security Affairs10일 전APT·위협행위자
 Bitget Says Suspected North Korean Hackers Stole $351.6M After Backend CompromiseCryptocurrency exchange Bitget said suspected North Korean threat actors have stolen $351.6 million from its hot and warm wallets. "At 18:31 UTC on September 24, 2026, Bitget's securit…The Hacker News10일 전APT·위협행위자
 Attackers Exploit WordPress CVE-2026-87902 Within Hours of DisclosureThreat actors have begun to actively exploit a critical security flaw in WordPress within hours of public disclosure. The vulnerability in question is CVE-2026-87902 (CVSS score: 9.2), which…The Hacker News11일 전취약점·패치APT·위협행위자CVE-2026-87902
 Hackers start exploiting critical WordPress flaw for code executionThreat actors have moved from probing WordPress sites vulnerable to CVE-2026-87902 to exploiting the flaw to write files to disk that execute shell commands when accessed. [...]BleepingComputer12일 전취약점·패치APT·위협행위자CVE-2026-87902
 Attackers Use Malicious Terraform Providers to Deliver Go Malware via HashiCorp RegistryCybersecurity researchers have disclosed Go-based malware distributed via two Go Modules and two Terraform providers, marking the first time threat actors are using the centralized repositor…The Hacker News12일 전APT·위협행위자악성코드
 Malicious AI agents steal 600K credit cards, infect 100+ sites with skimmersA financially motivated threat actor is using open-source AI agent frameworks to attack hundreds of online retailers at scale, stealing more than 600,000 credit card records. [...]BleepingComputer12일 전APT·위협행위자AI 보안
 Compromised MemTensor Packages Deliver sckit Credential Stealer via npm and PyPIUnknown threat actors have managed to compromise two legitimate MemTensor packages across the npm and Python Package Index (PyPI) repositories to push a platform-specific Go-based implant du…The Hacker News12일 전APT·위협행위자클라우드·인프라
 Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP MalwareA Chinese threat actor codenamed UTA0565 has been observed exploiting the recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days through fake websites. The attacks, de…The Hacker News12일 전취약점·패치APT·위협행위자CVE-2026-85046CVE-2026-85880CVE-2026-87491
 Chinese hackers exploit WordPress, Zyxel flaws to steal govt dataA Chinese-speaking threat actor has been exploiting vulnerabilities in ZyXEL GS1900 Smart Managed Switches and WordPress to steal sensitive data from 996 devices and more than 18,500 records…BleepingComputer13일 전취약점·패치APT·위협행위자
 Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before RemovalA malicious npm package named "indexed-btree" has been observed hiding its malicious behavior within application code rather than using lifecycle scripts, indicating that threat actors are l…The Hacker News13일 전APT·위협행위자
 SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-PhishingThe threat actor known as SideCopy has been observed using spear-phishing lures to target academic institutions in India, expanding their strategic focus beyond government entities. "SideCop…The Hacker News13일 전피싱·사기APT·위협행위자
 Contagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in CryptoThe North Korean threat actors behind the Contagious Interview campaign have compromised at least 30,000 devices located in more than 100 countries and siphoned funds or account credentials …The Hacker News14일 전APT·위협행위자
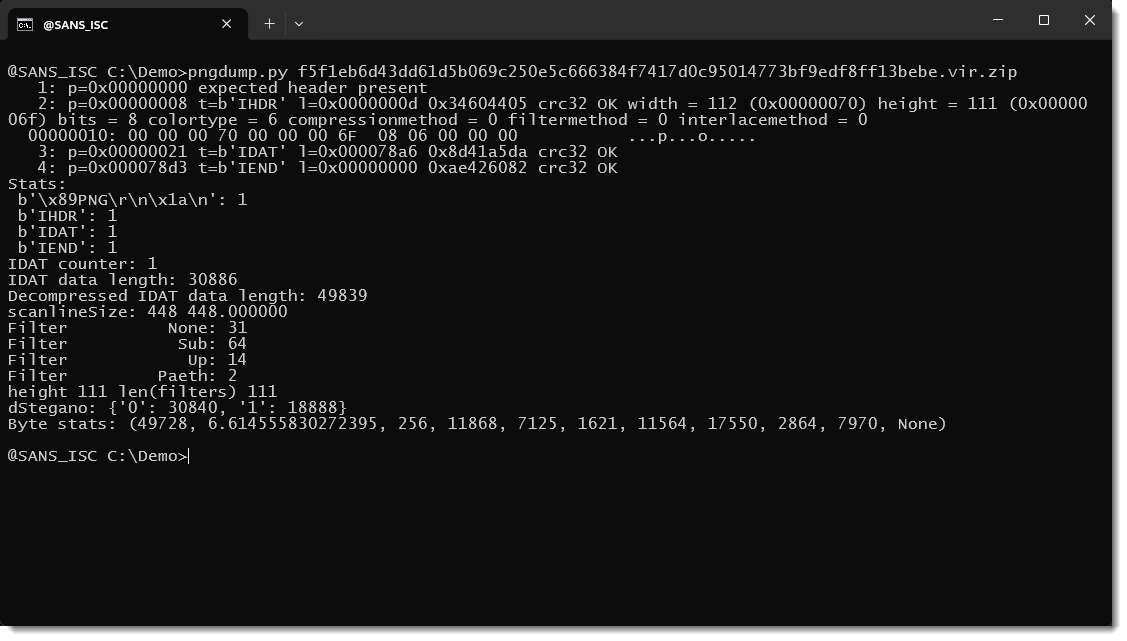 TerminalFix: PNG Steganography, (Mon, Sep 21st)Microsoft Security Research published an interesting blog post " TerminalFix campaign deploys a reverse tunnel through multistage intrusion " about a malware campaign. The aspect t…SANS Internet Storm Center14일 전APT·위협행위자악성코드
 ClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 InfrastructureThreat actors are leveraging ClickFix-like lures to deliver a previously undocumented remote access trojan (RAT) called ChainScript. "ChainScript has appeared under multiple build names, inc…The Hacker News14일 전APT·위협행위자악성코드
 Jade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK BackdoorsThe North Korean threat actor known as Jade Sleet has been attributed to the compromise of an India-based "much smaller organization" in the information technology (IT) services industry, on…The Hacker News14일 전유출·침해APT·위협행위자
 Malicious npm packages evade install-script defenses at runtimeAn ongoing npm malware campaign involving the 'indexed-btree' package shows how threat actors bypass supply chain defenses by hiding malicious code in a package's normal runtime behavior rat…BleepingComputer15일 전APT·위협행위자악성코드
 SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 115Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Gray Rabbits and the Tale of a One-Cl…Security Affairs15일 전APT·위협행위자악성코드
 Gyazo Data Breach Exposes 23 Million User RecordsA Gyazo breach exposed 23 million user records after attackers exploited a vulnerability in Helpfeel’s image upload server. Japanese software company Helpfeel is notifying Gyazo users about …Security Affairs17일 전취약점·패치유출·침해
 Claimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm StealerA financially motivated threat actor has been linked to the development and distribution of a JavaScript (JS)-based information stealer known as PhantomRaven via the npm package registry. "T…The Hacker News17일 전APT·위협행위자악성코드
 RatHat Android Malware Abuses ADB to Retain Shell Access After UninstallCybersecurity researchers have flagged a new Android malware called RatHat that's assessed to be operated by China-based threat actors and features an artificial intelligence (AI)-powered sy…The Hacker News17일 전피싱·사기APT·위협행위자
 China-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin AmericaThe China-aligned state-sponsored threat actor known as FamousSparrow has been observed deploying a previously unreported backdoor called SparroWocky in attacks targeting multiple countries …The Hacker News18일 전APT·위협행위자악성코드
 Three Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and WipersEnterprises in Russia have emerged as the target of three threat activity clusters tracked as NightEagle, Hacking Cat, and Toy Ghouls, according to multiple reports from Kaspersky. The cyber…The Hacker News19일 전랜섬웨어APT·위협행위자
 Revolut Data Leak May Trace Back to Compromised Italian Government AccountsA suspected compromise of an Italian government PEC account may have allowed threat actors to impersonate law enforcement and obtain sensitive data from hundreds of Revolut customers. The Re…Security Affairs19일 전유출·침해APT·위협행위자
 N0va Phishkit Targets US and EU Businesses: A New Challenge for Identity SecurityN0va is targeting organizations across North America and Europe with phishing campaigns that impersonate trusted services and abuse legitimate authentication flows. Successful attacks can gi…The Hacker News19일 전피싱·사기APT·위협행위자
 Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web ShellsThreat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. "This vulnerability can be l…The Hacker News19일 전취약점·패치APT·위협행위자
 Malcious Admin Menu Editor Pro plugin backdoors 1,500 WordPress sitesMalicious versions of the Admin Menu Editor Pro plugin for WordPress have been distributed to more than 200 customers after a threat actor compromised the maintainer's website and pushed upd…BleepingComputer20일 전APT·위협행위자악성코드
 KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session TokensCybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activ…The Hacker News20일 전APT·위협행위자악성코드
🔌 피드 상태
죽은 피드를 목록에서 지우지 않습니다. 지우면 왜 빠졌는지 잊고 다음 사람이 다시 추가합니다.
| 피드 | 구분 | 상태 | 최근 항목 | 비고 |
|---|---|---|---|---|
| ASEC 분석 리포트 | 국내 · 보안기업 | 정상 | 30 | 실측 30건. 국내 표적 악성코드 분석이 가장 두껍다. |
| KrCERT 보안공지 | 국내 · 기관 | 정상 | 10 | 보호나라와 같은 게시판이다. 권고 본문·CVE 연결은 lib/kisa 가 따로 다룬다. |
| S2W Blog | 국내 · 보안기업 | 정상 | 10 | 실측 10건. 다크웹·위협 인텔리전스. |
| 데일리시큐 | 국내 · 매체 | 정상 | 50 | 실측 50건. |
| 이스트시큐리티 알약 블로그 | 국내 · 보안기업 | 정상 | 50 | 실측 50건. |
| 지니언스 시큐리티 센터 | 국내 · 보안기업 | 정상 | 10 | 실측 10건. |
| SK쉴더스 | 국내 · 보안기업 | 차단됨(403) | 403 (봇 차단). 우회하지 않는다 — 거부 의사 표시다. 링크만 다룬다. | |
| 보안뉴스 | 국내 · 매체 | 경로 불명 | news_rss.xml 이 200 을 주지만 홈으로 리다이렉트되어 항목 0건. 경로 재조사 대상. | |
| 이글루코퍼레이션 | 국내 · 보안기업 | 경로 불명 | 연결 실패(HTTP 000). 피드 경로 미확인. | |
| 하우리 | 국내 · 보안기업 | 경로 불명 | 404 — 피드 경로 미확인. | |
| BleepingComputer | 해외 · 매체 | 정상 | 15 | |
| Google Project Zero | 해외 · 보안기업 | 정상 | 10 | googleprojectzero.blogspot.com 은 302 로 이 주소로 옮겨졌다. 옛 주소를 쓰면 항목 0건. |
| Krebs on Security | 해외 · 매체 | 정상 | 10 | |
| SANS Internet Storm Center | 해외 · 기관 | 정상 | 10 | |
| Schneier on Security | 해외 · 매체 | 정상 | 10 | |
| Security Affairs | 해외 · 매체 | 정상 | 10 | |
| The Hacker News | 해외 · 매체 | 정상 | 50 | |
| CISA Cybersecurity Advisories | 해외 · 기관 | 차단됨(403) | 피드가 403. 다만 **KEV JSON 은 정상**이라 핵심 데이터는 확보돼 있다. | |
| Microsoft MSRC Blog | 해외 · 보안기업 | 경로 불명 | 301 → HTML 페이지. RSS 경로 미확인. |
403(거부)과 404(경로 변경)는 대응이 다릅니다. 403 은 우회하지 않습니다 — 보안 사이트가 봇 차단을 우회하는 것은 그 자체로 모순입니다.
HTTP 200 인데 항목이 0건인 피드가 있습니다. 응답 코드만 보면 정상으로 집계되어, 수집이 멈춘 것을 몇 주 뒤에 알게 되는 유형입니다 — 그래서 항목 수까지 저장해 화면에 그대로 드러냅니다. 현재 빈 피드 0개 · 수집 불가 6개.